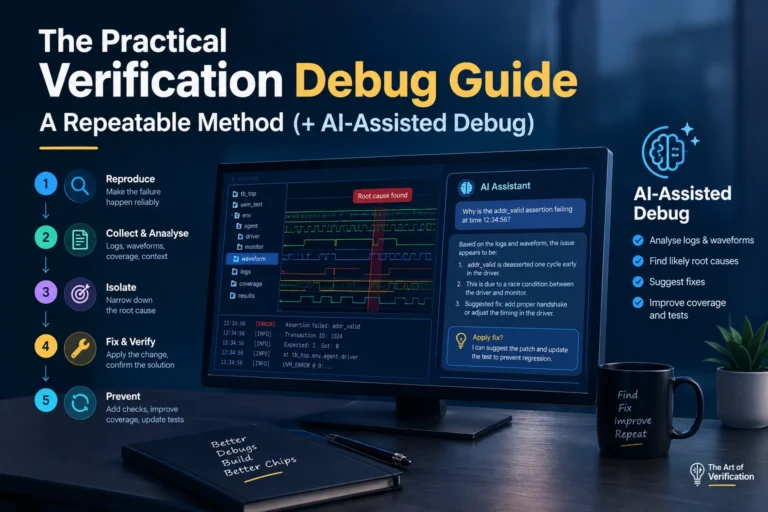
The Practical Verification Debug Guide: A Repeatable Method (+ AI-Assisted Debug)
A repeatable verification debug method: the five-door order, UVM and SystemVerilog tips, waveform tracing, regression triage, and an AI-assisted debug flow.
A repeatable verification debug method: the five-door order, UVM and SystemVerilog tips, waveform tracing, regression triage, and an AI-assisted debug flow.
In the fast-moving business of chip design, where logic and silicon come together to power the devices we rely on every day, a group of quiet problem solvers does the careful work behind the scenes: ASIC verification engineers. These are the people who chase down bugs before a chip ever reaches production, testing every path…
In short: Designs need many clock frequencies from one reference. Division is simple but only gives integer ratios below the reference and can pile up jitter across a long chain. Multiplication, usually via a PLL, reaches higher frequencies, supports non-integer ratios, and often has lower jitter, which is why it suits high-speed links, CPU cores,…
In short: Formal and functional verification are partners. Formal uses mathematics to prove a property holds for every possible case, which fits small control logic and safety-critical corners. Functional runs simulations across many realistic scenarios and scales to a full system, but it can only sample the state space. Strong teams use formal for the…
In short: A verification plan is the map for the whole effort. It lists every feature to check, ranks them by risk, matches each to the right stimulus and technique, and ties coverage goals and a schedule to them so problems appear early. Read the spec first, blend random, directed, and environment-driven stimulus, track coverage…
In short: Formal verification uses mathematics to prove a design property is always true, for every possible input, instead of checking a few cases with simulation. It pays off most when you apply it function by function, not block by block: pick the parts that are hard to cover in simulation, carry the most risk,…
In short: This is a hands-on tour of SystemVerilog assertions examples using the most-used building blocks: the delay operator ##, overlapping |-> and non-overlapping |=> implication, delay ranges ##[m:n], and the edge detectors $rose and $fell. Each one is shown with a small property, when it passes, and, more importantly, when it fails. Good assertions…
In short: An immediate assertion checks a condition the moment the simulator reaches it in procedural code, like a plain if-check. A concurrent assertion checks behaviour over time, sampling signals on a clock edge and spanning one or more cycles. Use immediate for a quick single-point check, and concurrent for anything that involves “on the…
In short: An assertion is a small rule that describes how a design should behave. If the design breaks the rule during simulation, the assertion fails and points you straight to the problem. The big advantages are early bug detection, better visibility into what went wrong, reuse in both simulation and formal tools, and a…
In short: SVA bind lets you attach assertions to a design module without editing that module. You write your checkers in a separate assertion module, then use the bind keyword to connect them to a target module or a specific instance. The design source stays untouched, which is ideal when you are not allowed to…