rand_mode vs constraint_mode in SystemVerilog: Freeze a Variable or Drop a Rule
In short: rand_mode() turns one random variable on or off. When it’s off, randomize() leaves that variable’s value alone. constraint_mode() turns one constraint block on or off. When it’s off, the solver ignores that rule. They are independent: freezing a variable does not switch off the constraints that use it, which is why randomize() often fails right after a rand_mode(0).
Sooner or later every testbench needs a test that’s “random, except for this one thing”.
Same address every time. Or one rule broken on purpose, to see if the design catches it.
SystemVerilog gives you two switches for that. They sound alike, but they do very different jobs.
Think of it like a board game
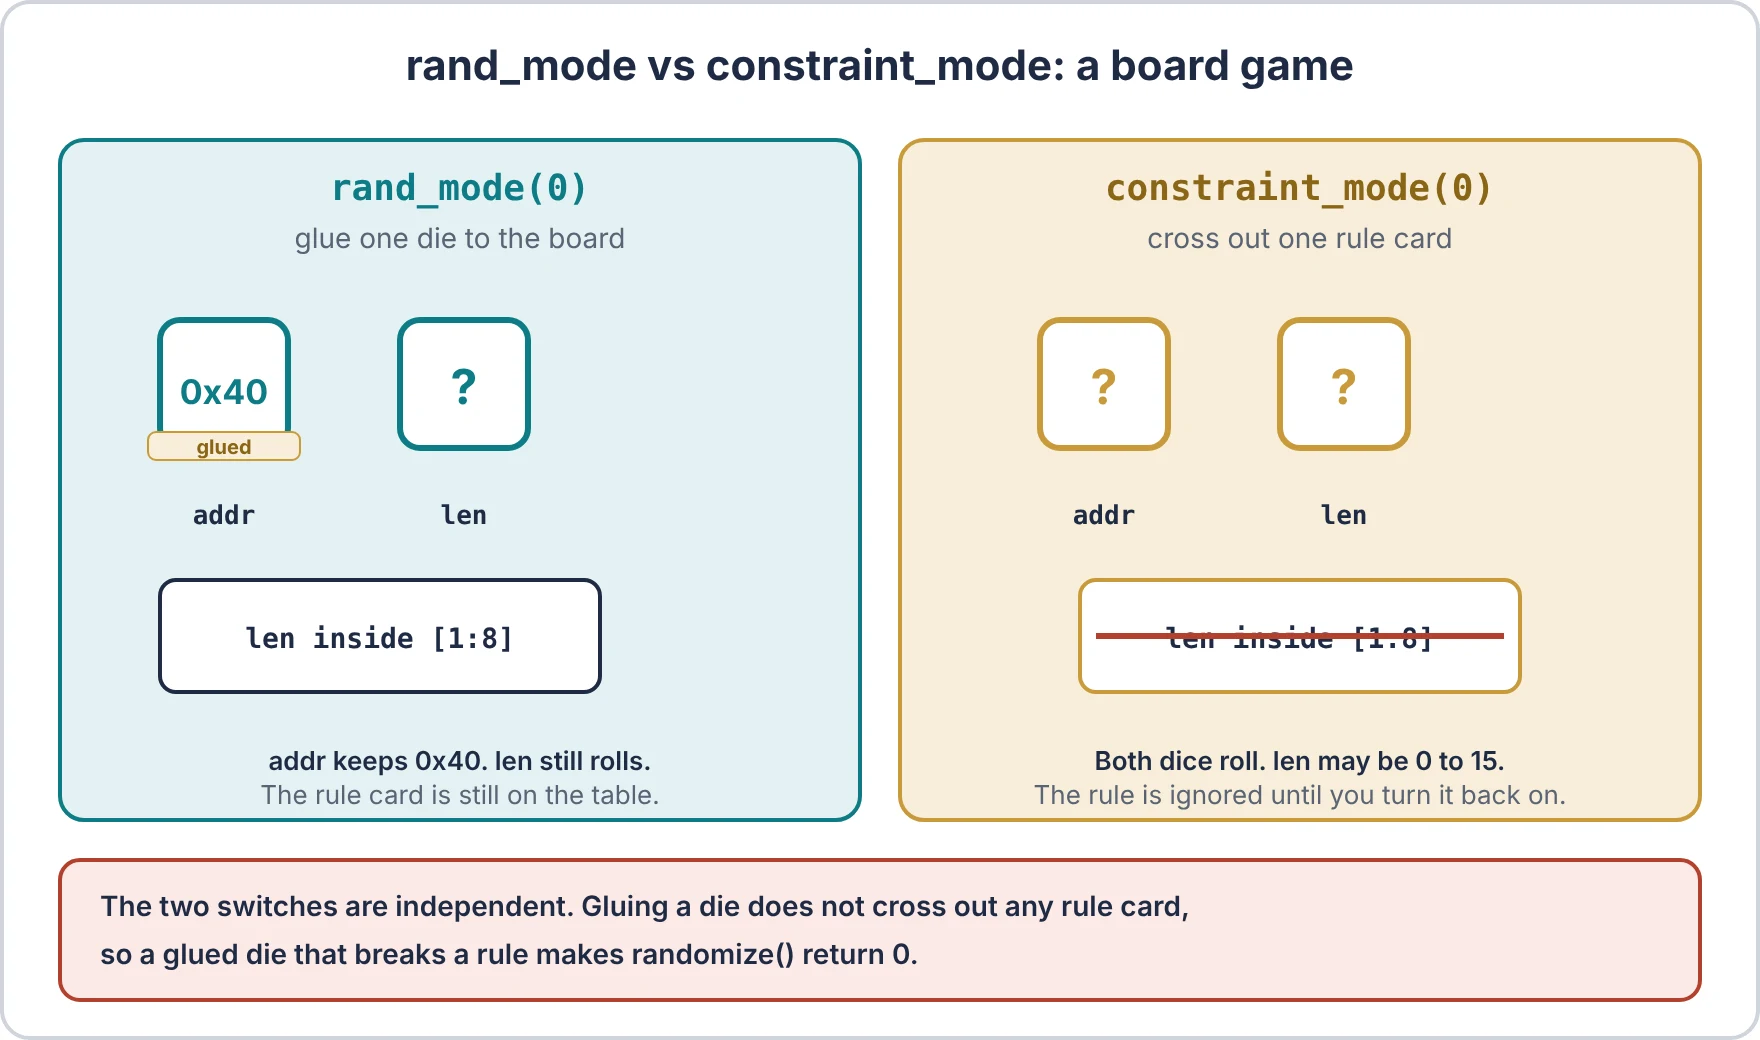
Picture a board game with dice and a stack of rule cards.
- **The dice are your
randvariables.** Every turn (everyrandomize()call), you roll them. - The rule cards are your constraint blocks. “The red die must be lower than the blue die.”
- **
rand_mode(0)glues one die to the board.** It keeps showing whatever face it has. It won’t roll anymore. - **
constraint_mode(0)crosses out one rule card.** Nobody has to follow it until you un-cross it.
Here’s the catch, and it’s the source of most forum questions. Gluing a die does not cross out any rule cards. If the glued die breaks a rule that’s still active, the turn can’t be played. That’s randomize() returning 0.
rand_mode(): freeze one variable
class packet;
  rand bit [7:0] addr;
  rand bit [3:0] len;
  constraint c_len { len inside {[1:8]}; }
endclass

module tb;
  initial begin
    packet p = new();
    p.addr.rand_mode(0);          // freeze addr: it is now a plain value
    p.addr = 8'h40;
    repeat (3) begin
      if (!p.randomize()) $error("randomize failed");
      $display("addr=%h len=%0d", p.addr, p.len);
    end
    $display("addr rand_mode = %0d, len rand_mode = %0d",
             p.addr.rand_mode(), p.len.rand_mode());
    $finish;
  end
endmodule
Expected output (per IEEE 1800-2017, section 18.8; see the code note at the end):
- Three lines, all with
addr=40.lenis a new value from 1 to 8 on each line. - The last line reads
addr rand_mode = 0, len rand_mode = 1.
What to notice:
p.addr.rand_mode(0)is the task form: it sets the switch.p.addr.rand_mode()with no argument is the function form: it reads the switch and returns 1 or 0.p.rand_mode(0)with no variable name switches off every random variable in the object.
constraint_mode(): drop one rule
class packet;
  rand bit [7:0] addr;
  rand bit [3:0] len;
  constraint c_len { len inside {[1:8]}; }
endclass

module tb;
  initial begin
    packet p = new();
    p.c_len.constraint_mode(0);   // drop the rule: len may now be 0 to 15
    repeat (3) begin
      if (!p.randomize()) $error("randomize failed");
      $display("len=%0d", p.len);
    end
    $display("c_len constraint_mode = %0d", p.c_len.constraint_mode());
    p.c_len.constraint_mode(1);   // rule back on for the next test
    $finish;
  end
endmodule
Expected output (per IEEE 1800-2017, section 18.9):
- Three values of
lenanywhere from 0 to 15, because the 1-to-8 rule is gone. - The last line reads
c_len constraint_mode = 0.
What to notice:
p.c_len.constraint_mode(0)switches off one block.p.constraint_mode(0)switches off all of them.- Turn it back on when the test is done. The switch stays where you left it, for every later
randomize()on that object.
The trap: a frozen variable still has to obey the rules
class packet;
  rand bit [7:0] addr;
  rand bit [3:0] len;
  constraint c_len { len inside {[1:8]}; }
endclass

module tb;
  initial begin
    packet p = new();
    p.len.rand_mode(0);
    p.len = 12;                   // frozen, but outside [1:8]
    if (!p.randomize())
      $display("randomize() returned 0: c_len still applies to the frozen len");
    p.c_len.constraint_mode(0);   // drop the rule too
    if (p.randomize())
      $display("randomize() returned 1: len=%0d stays, addr=%h is new", p.len, p.addr);
    $finish;
  end
endmodule
Expected output (per IEEE 1800-2017, sections 18.3 and 18.8):
- First
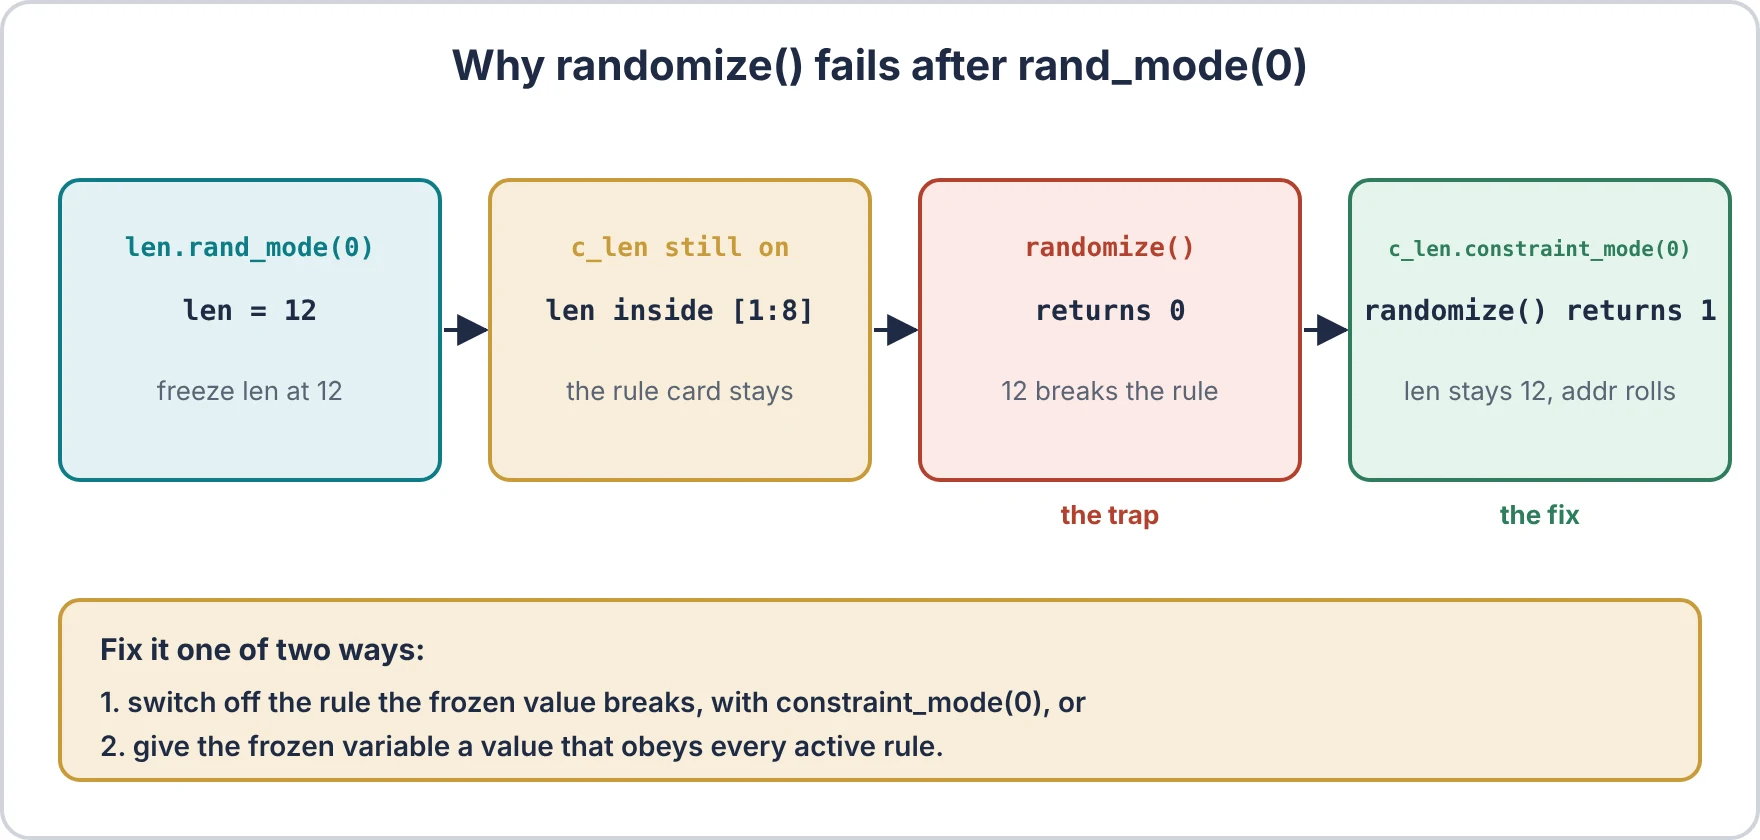
randomize()returns 0. The frozenlen = 12breaksc_len, which is still on. - After
c_len.constraint_mode(0),randomize()returns 1.lenstays 12 andaddrgets a new random value.
That’s the glued die breaking an active rule. Most simulators also print a solver warning naming c_len.
rand_mode vs constraint_mode, side by side
rand_mode() | constraint_mode() | |
|---|---|---|
| Works on | A rand or randc variable (or the whole object) | A constraint block (or the whole object) |
| When off | The variable keeps its value; the solver treats it as a fixed number | The solver ignores that block |
| Board-game picture | Glue a die to the board | Cross out a rule card |
| Does it switch off the other one? | No. Constraints on a frozen variable still apply | No. Variables in a dropped rule still get randomized |
| Read the current state | obj.var.rand_mode() returns 1 or 0 | obj.c_name.constraint_mode() returns 1 or 0 |
| Typical use | Fix a field for a directed test, or take a value from the command line | Allow an illegal value for a negative test, or swap one rule for another |
| IEEE 1800-2017 | Section 18.8 | Section 18.9 |
A third switch: randomize() with arguments
You can also name the variables to randomize right in the call:
p.randomize(len)randomizes onlylenthis time. Every other variable is treated as frozen for this one call, whatever itsrand_modesays.p.randomize(null)randomizes nothing. It only checks that the current values meet every active constraint, which is a handy self-check.
This is section 18.11 of the standard. Use it for a one-off; use rand_mode() when the change should last.
A working example: two AXI tests from one transaction class
This ties back to the 4KB rule and unique AXI IDs.
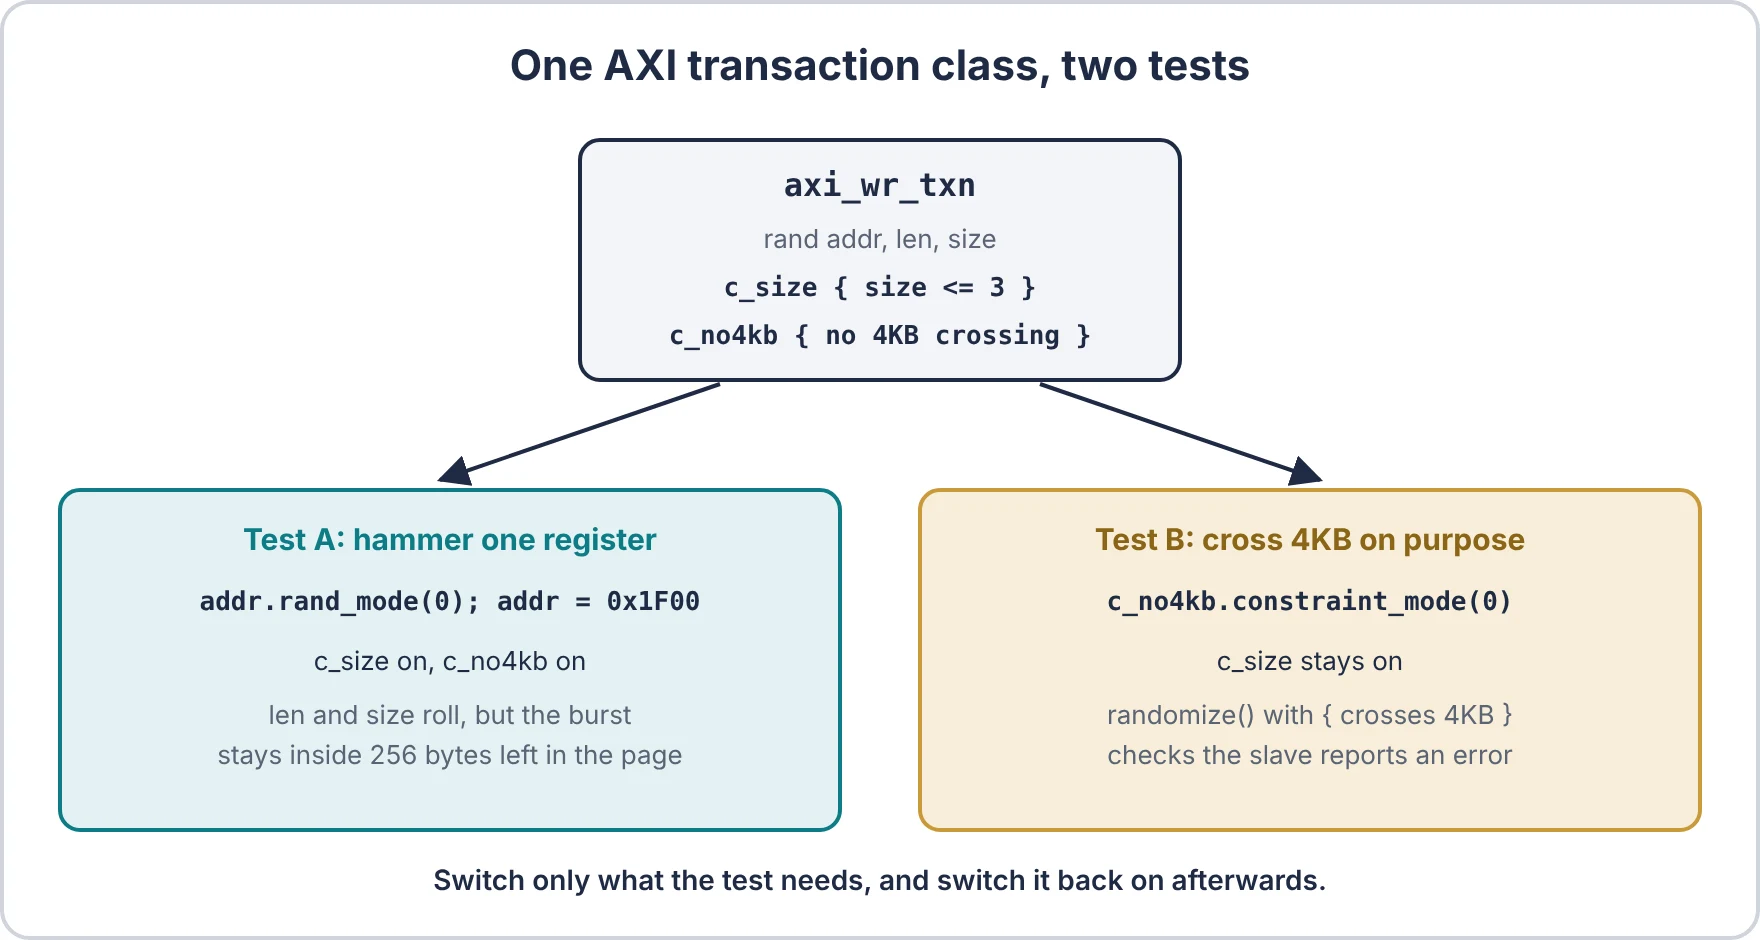
One AXI write transaction class has two rules: a legal beat size, and no burst may cross 4KB. Two tests reuse it:
- Test A: hammer one register at 0x1F00 with random lengths. Freeze the address with
rand_mode(0). - Test B: a negative test where the burst must cross 4KB, so we can check the slave reports an error. Drop the 4KB rule with
constraint_mode(0)and ask for a crossing.
// An AXI write transaction with two rules: legal length, and no 4KB crossing.
class axi_wr_txn;
  rand bit [31:0] addr;
  rand bit [7:0]  len;                       // AWLEN: beats - 1
  rand bit [2:0]  size;                      // AWSIZE: 2**size bytes per beat
  constraint c_size  { size <= 3; }          // up to 8 bytes per beat on a 64-bit bus
  constraint c_no4kb { addr % 4096 + ((len + 1) << size) <= 4096; }
endclass

module tb;
  initial begin
    axi_wr_txn t = new();

    // Test A: hit one register address again and again, everything else random.
    t.addr.rand_mode(0);
    t.addr = 32'h0000_1F00;
    repeat (2) begin
      if (!t.randomize()) $error("A: randomize failed");
      $display("A: addr=%h len=%0d size=%0d", t.addr, t.len, t.size);
    end
    t.addr.rand_mode(1);

    // Test B: a negative test that must cross 4KB, to check the slave reports an error.
    t.c_no4kb.constraint_mode(0);
    if (!t.randomize() with { addr % 4096 + ((len + 1) << size) > 4096; })
      $error("B: randomize failed");
    $display("B: addr=%h len=%0d size=%0d (crosses 4KB on purpose)", t.addr, t.len, t.size);
    t.c_no4kb.constraint_mode(1);
    $finish;
  end
endmodule
Expected output (per IEEE 1800-2017):
- Two “A” lines with
addr=00001f00. Because 0x1F00 is 3,840 bytes into its 4KB page, only 256 bytes are left, so the solver keeps(len + 1) x 2**sizeat 256 or less. - One “B” line where the burst runs past the end of its 4KB page.
What makes this work:
- Test A freezes the address, but
c_no4kbstays on. So the glued die and the rule cards still agree, and the solver simply picks shorter bursts. - Test B crosses out exactly one rule card and keeps
c_size. Turning off everything witht.constraint_mode(0)would also let illegal beat sizes through, and the negative test would fail for the wrong reason. - Both tests switch things back on at the end, so the next test starts clean.
Common mistakes (and the fix for each)
These come from real Verification Academy threads. Each one is retold in my own words, with a link to the original.
1. Expecting rand_mode(0) to switch off the constraints
- What happened: in 2016 an engineer set
a = 5andb = 1, froze both withrand_mode(0), and calledrandomize()with a constrainta < b. It failed (Verification Academy, 2016). - Why: constraints stay active even when every variable in them is frozen (IEEE 1800-2017, 18.3 and 18.8).
- Fix: also switch off the rule with
constraint_mode(0), or set values that obey it.
2. Freezing a field in pre_randomize, inside a UVM override
- What happened: in 2021 someone fixed an enum to TRANSMIT in an overridden
pre_randomize()withrand_mode(0). A constraint said that whenidis even, the enum must be RECEIVE.idwas 0, so the solver failed (Verification Academy, 2021). - Why: same trap: the frozen value broke a rule that was still on. It’s harder to spot because the rule lived in the base class.
- Fix: switch off the conflicting constraint too, ideally in the extended class’s constructor.
3. Overwriting values in pre_ or post_randomize to inject command-line values
- What happened: in 2024 an engineer wanted
aandbto come from plusargs. Setting them inpost_randomize()could breaka > b; setting them inpre_randomize()got overwritten (Verification Academy, 2024). - Fix: in
pre_randomize(), read the plusarg and freeze only if it was given:if ($value$plusargs("VALUE_A=%0d", a)) a.rand_mode(0);. Rules still apply, so a bad value on the command line makesrandomize()fail loudly instead of slipping through.
4. Turning off a static constraint for one object
- What happened: in 2022 someone called
constraint_mode(0)on astaticconstraint through one object and was surprised by the result (Verification Academy, 2022). - Why: a static constraint is shared. Switching it off through one object switches it off for every object of that class.
- Fix: only make a constraint
staticwhen you really want one switch for all objects. Otherwise leave it per-object.
5. rand_mode(0) on a dynamic array
- What happened: in 2015 an engineer froze a
randdynamic array withrand_mode(0), but it still got randomized. The same call worked on a fixed-size array, and different simulators behaved differently (Verification Academy, 2015). - Why: a dynamic array has a random size as well as random elements, and tools have disagreed on how
rand_modeapplies to both. - Fix: size the array yourself first, switch off any size constraint, freeze the elements, and check the result on your own simulator.
6. Reading rand_mode() inside a constraint
- What happened: in 2019 someone used
if (sv.rand_mode() == 1)as a guard inside a constraint. Only some simulators accepted it (Verification Academy, 2019). - Why: the standard forbids changing modes inside a constraint, but reading one isn’t clearly covered, so tool support varies.
- Fix: keep it portable. Use a plain non-random flag (
bit fixed_sv;) as the guard and set it next to therand_mode()call.
Frequently asked questions
What is the difference between rand_mode and constraint_mode?
rand_mode() decides whether a variable gets a new random value. constraint_mode() decides whether a rule is enforced. One freezes values, the other drops rules, and neither touches the other.
Why does randomize() fail after rand_mode(0)?
The frozen value breaks a constraint that is still on. Switch that constraint off, or give the variable a legal value.
How do I disable randomization for one variable only?
obj.var.rand_mode(0); Or, for a single call, obj.randomize(other_vars) with only the variables you want randomized.
How do I check if a constraint is on?
obj.c_name.constraint_mode() returns 1 if it’s on, 0 if it’s off.
Does rand_mode(0) on the object switch off constraints?
No. obj.rand_mode(0) freezes every variable, but all constraints are still checked.
Do I need to switch modes back on?
Yes, if the object is reused. The switches stay where you left them for every later randomize() call.
What to read next
- How to generate an array of unique random values
- AXI protocol explained: where the 4KB rule comes from
References
- IEEE 1800-2017, SystemVerilog standard: section 18.3 (constraint concepts), 18.5.11 (static constraint blocks), 18.8 (rand_mode), 18.9 (constraint_mode), 18.11 (in-line random variable control).
- Verification Academy forum threads linked in the mistakes section (accessed 6 Nov 2026).
Code note: the examples follow IEEE 1800-2017 but were not simulated here, because Verilator 5.020 ignores rand_mode() and constraint_mode(). Run them on your simulator or EDA Playground to confirm.
Part of the learning path SystemVerilog for verification